
Apple Launches New Security Research Website To Better Reward Engineers

To expand the reach of its security research arm, Apple has launched Apple Security Research, a site allowing engineers to directly report possible issues to the company, and to provide more information on real-time status updates and security reports.
Aside from publishing information on its ongoing Apple Security Bounty programs, which reward volunteers who help to make its ecosystem safer for users, the site will double up as a blog for engineering experts to share the latest advancements in the technology.
According to Apple, it has awarded researchers nearly US$20 million in the past 2.5 years of the program—with an average payout of US$40,000 in the product category, and a whopping US$100,000 for high-impact issues.
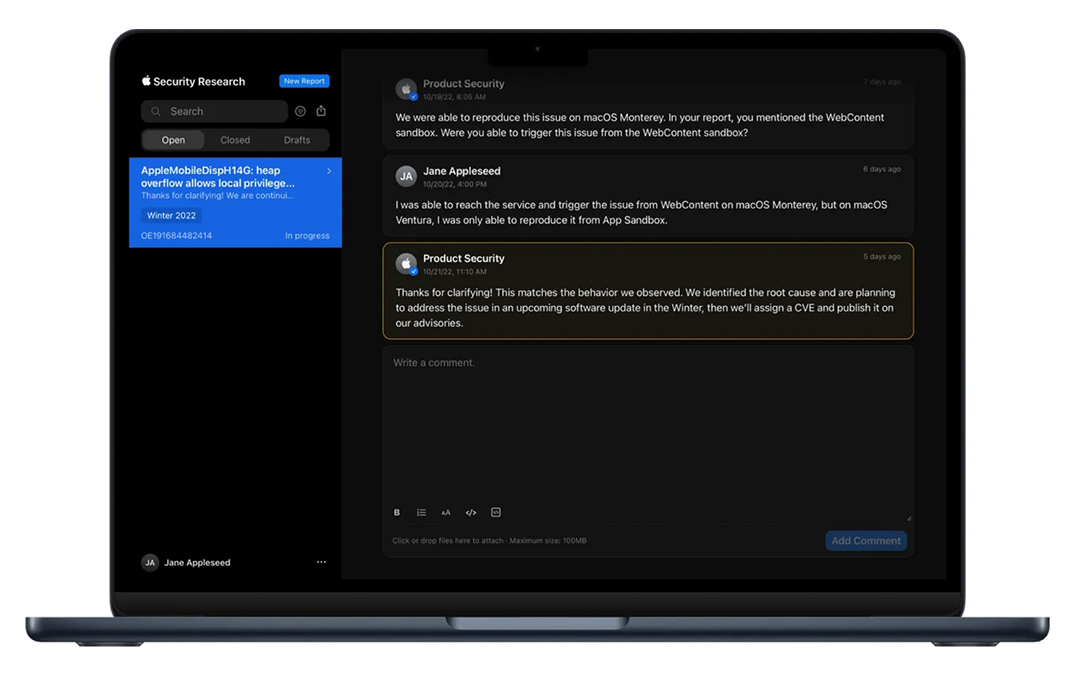
Now, to streamline the process for techies looking to contribute, the company has in place new measures to help it respond more quickly to submissions within two weeks, along with a new way to communicate directly with the teams with real-time tracking updates.
Those keen to get involved can submit their applications for the 2023 Apple Security Research Device Program from now through November 30, 2022. Accepted parties will receive a special iPhone specially designed for finding bugs and security loopholes to speed up research.
Head here for more information.


